PSPF physical security is a mandatory part of the framework that protects people, information and assets, and the mandatory items sit in the annual release, so check the latest PSPF Release 2025 before anything else. Your first move is to match your entity’s current self-assessed maturity against those requirements, then schedule a risk-based review of your facilities and controls.
TL;DR:
- Policies 4, 15, and 16 cover maturity monitoring, protection of entity resources, and facility management; guidelines remain optional and help determine how to comply.
- The 2024–25 assessment found that 92% of noncorporate Commonwealth entities reported Effective compliance and 8% Moderate; ratings rely on evidence.
- When budgets or heritage constraints limit upgrades, document procedures first, strengthen access records, then improve alarm response and physical barriers in stages.
- Connect physical and cyber controls through shared asset registers, coordinated access removal, common system patching, and joint incident exercises, including tailgating and stolen devices.
- Pilot biometric readers or video analytics in one area, track false acceptance and alarms, and define human review and override before wider adoption.
Table of Contents
- Where does physical security sit in the PSPF structure?
- Which requirements are mandatory, and which are guidance?
- Who is accountable for physical security?
- How do risk, business impact levels and zoning work together?
- What does PSPF-aligned physical security look like on the ground?
- How do maturity levels and annual reporting work?
- How should physical and cyber security work together?
- What training and competency do your people need?
- How are biometrics and AI-enabled surveillance changing physical security?
- Which metrics show your physical security is working?
- Where integrated security delivers real progress
- How we can help your agency meet PSPF physical security needs
- FAQ
- Sources
Where does physical security sit in the PSPF structure?
The PSPF works through tiers. Principles sit at the top, followed by security domains (physical security is one), policy requirements, standards and technical manuals, and finally best-practice guidelines. Knowing which tier a document belongs to tells you whether you must act on it or may adapt it. The PSPF Annual Release explains that the framework is reviewed annually, and that the latest major release is PSPF Release 2025, published on 24 July 2025.
Physical security does not stand alone. Good governance decides who owns a risk, personnel security decides who gets through the door, and information security decides what happens once they are inside. A weak lock on a records room undermines all three. Treat the physical domain as the layer that makes the other outcomes believable, and read the release with that in mind.
Which requirements are mandatory, and which are guidance?
Mandatory requirements live in the annual release, and non-corporate Commonwealth entities report on their compliance with them. The ANAO’s audit of the revised framework points to policies 4, 15 and 16 as the ones most relevant to physical security. In practical terms:
- Policy 4 covers security maturity monitoring: knowing where you stand and being able to show it.
- Policy 15 covers physical security for entity resources: protecting people, information and assets from foreseeable harm.
- Policy 16 covers entity facilities: how your buildings and zones are designed, built and managed.
The PSPF Release 2025 list of requirements shows each mandatory item and the reporting question attached to it. The PSPF Guidelines are different: they offer best-practice advice, they are optional, and you should apply them using a risk-based approach. Use them to decide how to meet a requirement, not whether to.
Who is accountable for physical security?
Check your entity’s governance arrangements to establish who is accountable for PSPF compliance and which responsibilities can be delegated. If your entity has a Chief Security Officer (CSO), consider coordinating facility upgrades, guarding contracts and access decisions as one program rather than separate projects.
Support sits outside your entity too. The Attorney-General’s Department publications library is a place to look for PSPF guidance. For technical advice, ASIO’s T4 Protective Security capability provides expert advice, training and evaluation of physical security products such as locks, alarms and detection devices. Before you specify a safe or a detection device for a sensitive area, check what T4 has evaluated.
How do risk, business impact levels and zoning work together?
Physical security under the PSPF is a risk-based exercise. The ANAO’s review of physical security management describes it as a mix of physical and procedural measures that create a safe and secure environment, with protective security built into day-to-day operations. You start by working out how badly a compromise would hurt, which gives you business impact levels, and those levels drive the protection you apply and the zones you create.
Zoning has consequences. A policy update on sensitive and classified information shows that some zones can restrict the handling of SECRET-rated information, and that entities may need a multi-year transition, in that case a 24-month window, to upgrade infrastructure. Check the current policy for specifics rather than relying on memory.
Your risk assessment should record:
- the assets, people and information in each area and their business impact levels
- the threats you considered and those you accepted
- why each zone sits where it does
- how each control choice ties back to a risk
Our security risk assessment checklist is a practical way to start or validate that record.
What does PSPF-aligned physical security look like on the ground?
Think in layers: perimeter, building, internal compartments, then secure storage. Each layer should slow or expose an intruder, and none should depend on a single control. A sensible sequence when budget or heritage buildings limit you:
- Document the current state and fix gaps in procedures, because they cost little and expose the most.
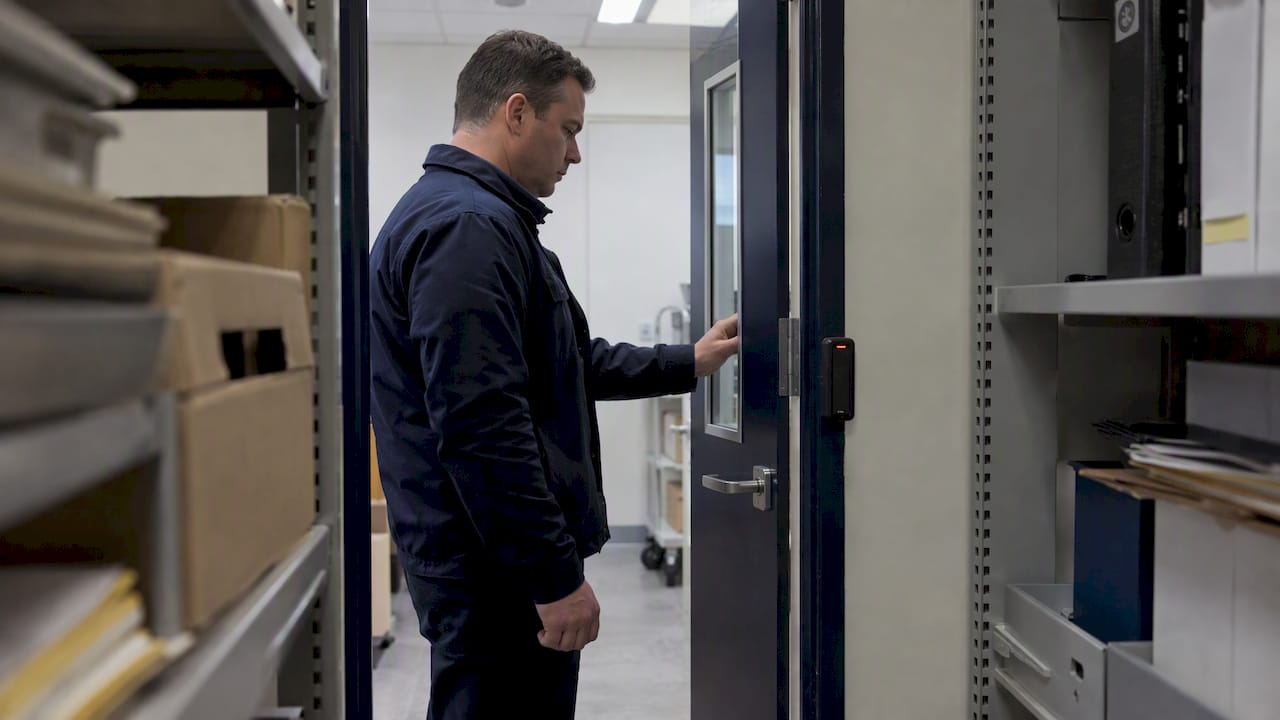
- Tighten access control, using role-based permissions, visitor management, vetting checks and proper records. Our guide to access control policies covers the policy side.
- Plan CCTV coverage and monitored alarm response so detection leads to action, not just footage.
- Upgrade physical measures such as locks, safes, secure rooms and barriers, using passive measures where a legacy building cannot take structural change.
- Set operational controls: guarding, patrols, contractor rules and incident procedures.
Keep change logs, test records and incident reviews for every step and feed them into your assurance plan. Evidence you can produce on demand is worth more than a control nobody can demonstrate.
Pro Tip: Test alarms and access logs on a schedule and file the results the same day, so your self-assessment is built from records rather than recollection.
For public-sector buildings, our decision-maker’s guide to government building security adds context. If your facility team is also coordinating site maintenance alongside security upgrades, this property protection example for ACT commercial sites shows how those works can be planned together.
How do maturity levels and annual reporting work?
The PSPF uses a maturity scale. The scale shows how consistently your controls operate, not just whether they exist. The PSPF Assessment Report 2024–25 was the first to use a compliance-based reporting model, with emphasis on evidence, risk outcomes and measurable assurance. In that cycle, 92% of non-corporate Commonwealth entities reported an overall rating of Effective compliance, and 8% reported Moderate.
A strong rating needs proof. Build a security assurance strategy that sets out what you monitor, who collects the evidence and when it is reviewed, so the annual self-assessment becomes a summary of work already recorded.
How should physical and cyber security work together?
Treat them as one security posture. A server room with excellent firewalls and a weak door is still an exposed server room, and a badge reader that logs to an unpatched system is a cyber risk wearing a physical uniform. The PSPF itself spreads outcomes across governance, information, personnel and physical domains, which is a hint that controls should be designed together.
In practice, start with shared asset registers so the team securing a room knows what digital assets sit in it. Align access reviews: when someone leaves or changes role, physical access and system access should be removed in the same process. Put access-control and CCTV systems on the same patching, logging and network-segmentation discipline as your other critical systems, and consider the security risks of network-connected devices. Finally, bring physical and cyber staff into the same incident exercises. A tailgating event that leads to a stolen laptop is a single incident, and your response plan should treat it as one.
Documenting these links also helps your assurance story. When an assessor asks how you know zoning decisions hold, you can show joined-up records rather than two separate stacks of paper, one per discipline.
What training and competency do your people need?
Controls only work when people operate them correctly. Everyone with a physical security role needs training matched to that role: security advisers who design zones, officers who run access control, guards on post, reception staff who manage visitors, and managers who approve exceptions. The PSPF Guidelines are optional best practice, so use them to shape your own competency framework, and use ASIO T4’s advice and training where your risks call for specialist knowledge.
A workable approach has four parts. First, induction that explains zones, escorting rules and how to report incidents. Second, role-specific training for those who handle alarms, keys, safes or classified material. Third, regular exercises so staff rehearse lockdowns, evacuations and alarm responses before they happen for real. Fourth, a record of who completed what and when, because competency you cannot evidence will not count at assessment time.

Contractors need the same attention. If a guarding or monitoring provider works inside your facility, specify any required licences, site-specific induction and refresher training in the contract, and check that the requirements are met. Our licensed guards, along with our patrol officers, work to those site requirements, and the provider you choose should be able to show you the same.
How are biometrics and AI-enabled surveillance changing physical security?
Biometric readers and video analytics promise stronger identity assurance and faster detection. Used well, they reduce reliance on easily shared cards and let a small control room watch more cameras. Used carelessly, they introduce privacy obligations, false alarms and new systems to secure.
The PSPF is a risk-based framework, so the test is the same as for any control: does it address a documented risk for a defined zone, and can you show it working? Before adopting a new technology, run a pilot in one area, record false acceptance and false alarm behaviour, and decide how a human will review and override automated decisions. Check what evaluation exists for the product, and ask ASIO T4’s protective security capability where physical security products are concerned.
Do not let technology paper over weak basics. Analytics on a camera that nobody monitors, or a biometric door beside an unlocked fire exit, adds cost and no assurance. Our electronic security solutions team designs systems on that principle: fix coverage, response and maintenance first, then layer in smarter detection where the risk warrants it.

Which metrics show your physical security is working?
Pick measures that prove outcomes, not just activity. Counting cameras installed tells you about spending, while measuring how fast an alarm is verified and answered tells you about security. Useful indicators include:
- time from alarm activation to verified response
- percentage of access rights reviewed on schedule
- visitor and contractor sign-in compliance
- number and type of unauthorised-access attempts and near misses
- completion rate for scheduled system tests and staff training
- time taken to close actions from audits and incident reviews
Tie each indicator to a requirement and a maturity target. If you are at “developing” for policy 15 and aim for “managing”, say what each metric must look like to justify moving up, and who reviews it. This is the sort of structured evidence the move to compliance-based reporting rewards.
Review the numbers on a fixed rhythm and record decisions made because of them. A metric that never triggers action is decoration. Our risk assessment process guide shows how to connect measures back to the risks they are meant to control.
Where integrated security delivers real progress
In our experience, agencies move toward managing and embedded maturity fastest when people, procedure and technology are planned as one system. Prioritise controls that generate evidence you can report, and write down every decision, owner and timeline, because the self-assessment rewards what you can show.
— Abco
How we can help your agency meet PSPF physical security needs
Lower the effort of proving compliance by working with a provider that handles design, delivery and monitoring together. We carry out security risk assessments, design and install electronic security solutions, run CCTV and alarm monitoring around the clock, and provide licensed security guarding and mobile patrol services.
Ask us for a security risk assessment of your facility, and we will map what you have against what you must evidence. Start at Abcosecurity.
FAQ
What is PSPF physical security?
PSPF physical security is the combination of physical and procedural measures that protect people, information and assets from foreseeable harm. The ANAO describes it as providing a safe and secure environment and requires a risk-based approach built into daily operations.
Which PSPF policies cover physical security?
Policies 4, 15 and 16 are the mandatory requirements most relevant to physical security, according to the ANAO. They cover security maturity monitoring, physical security for entity resources and entity facilities.
Are the PSPF Guidelines mandatory?
No. The PSPF Guidelines offer optional best-practice advice for meeting the requirements. Apply them using a risk-based approach and keep a record of why you chose a particular method.
Where do I find the current mandatory requirements?
They are in the annual release. Check the latest PSPF Release and its list of requirements before you finalise any compliance actions.
Sources
- Administration of the Revised Protective Security Policy Framework | Australian National Audit Office (ANAO)
- PSPF Annual Release 2025 | Protective Security Policy Framework
Recommended
about
avada factory
Sempery ultricies nibh at dolor cras urna eleifend nec. Atiam efficitur tempor.